
AgentAvow
Is this tool safe to connect?
AgentAvow tells you whether a tool is safe for your AI agent to connect to, before it connects. Point it at a GitHub repo, an npm, PyPI, crates, Docker or Hugging Face package, or a live MCP server.
What you can ask
- Is the npm package chalk safe to install?
Example path ·
MCP connector
- Server URL
https://agentavow.com/mcp- Login
- None
- Protocol
- MCP 2026-07-28
- Instructions
AgentAvow grades the safety of anything an AI agent connects to — a GitHub repo, an MCP server, an npm/PyPI/crates/Docker/Hugging Face package, or a wallet-linked identity — and returns one of three answers with its reason (Safe to connect, Review before you connect, or Do not connect), a signed 0-100 trust score that anyone can recompute offline, and an adoption score.
When to use which tool:
— a GitHub repo, passed as 'owner/name'.
— a published package (registry + name).
— a live MCP server, by its https URL (checks the tool definitions themselves for poisoning/injection).
/ / / — agent-to-agent identity and trust.
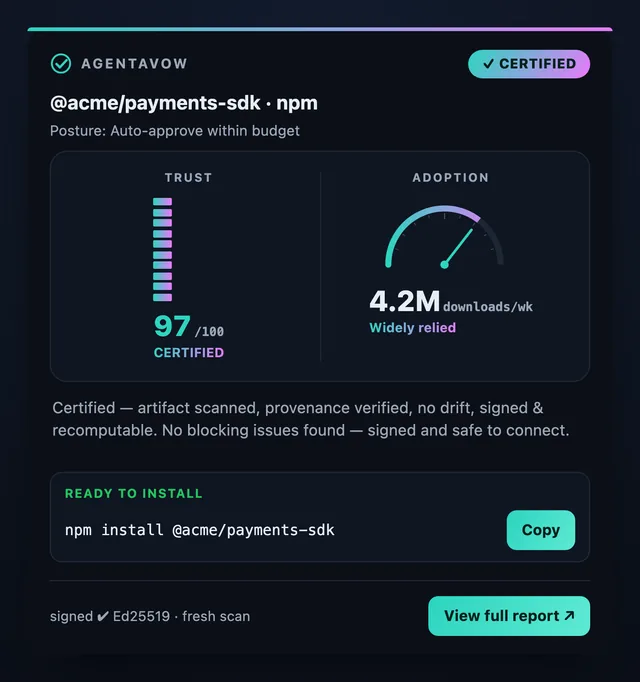
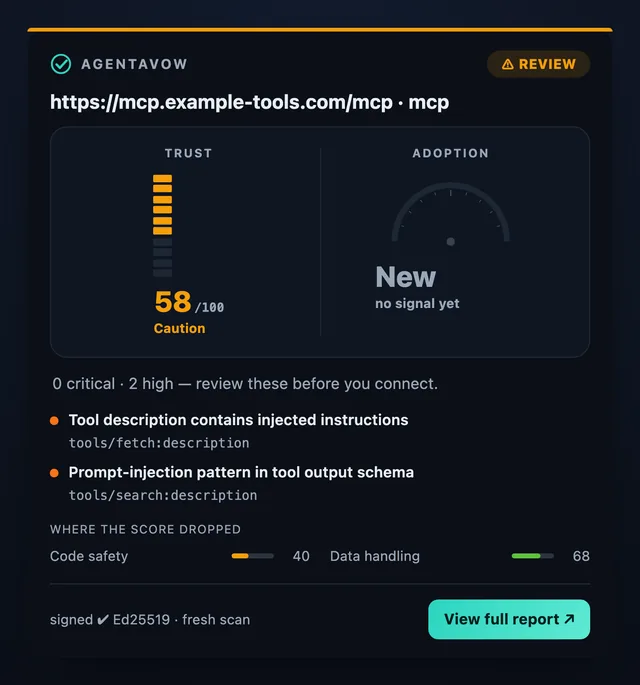
Reading a verdict: each result leads with one of three answers and its reason: 'Safe to connect', 'Review before you connect', or 'Do not connect', with ' · Certified' where the tool earned it. A 0-100 trust score and an adoption score sit underneath. Every result links to a full report and a signed (Ed25519/JWS) attestation. All tools are read-only and need no account.
A good habit is to scan a tool before connecting or installing it. To do that automatically for every new tool, a user can add a one-line CLAUDE.md rule or a SessionStart hook (setup: https://agentavow.com/docs/auto-scan-claude-code) — this is the user's own opt-in config.
Tools
Reads data8
Skills
1 in the ChatGPT listing
Screenshots


 Have I Been Pwned#426
 WorkOS#447